Software Supply Chain Risk When Agents Choose Your Dependencies: Provenance as a Release Gate
The largest security decision your team made this quarter was probably an import line an AI agent wrote in milliseconds. This post shows delivery leaders how software supply chain risk changed when agents started choosing dependencies, and how to turn dependency provenance into a release gate your pipeline enforces.
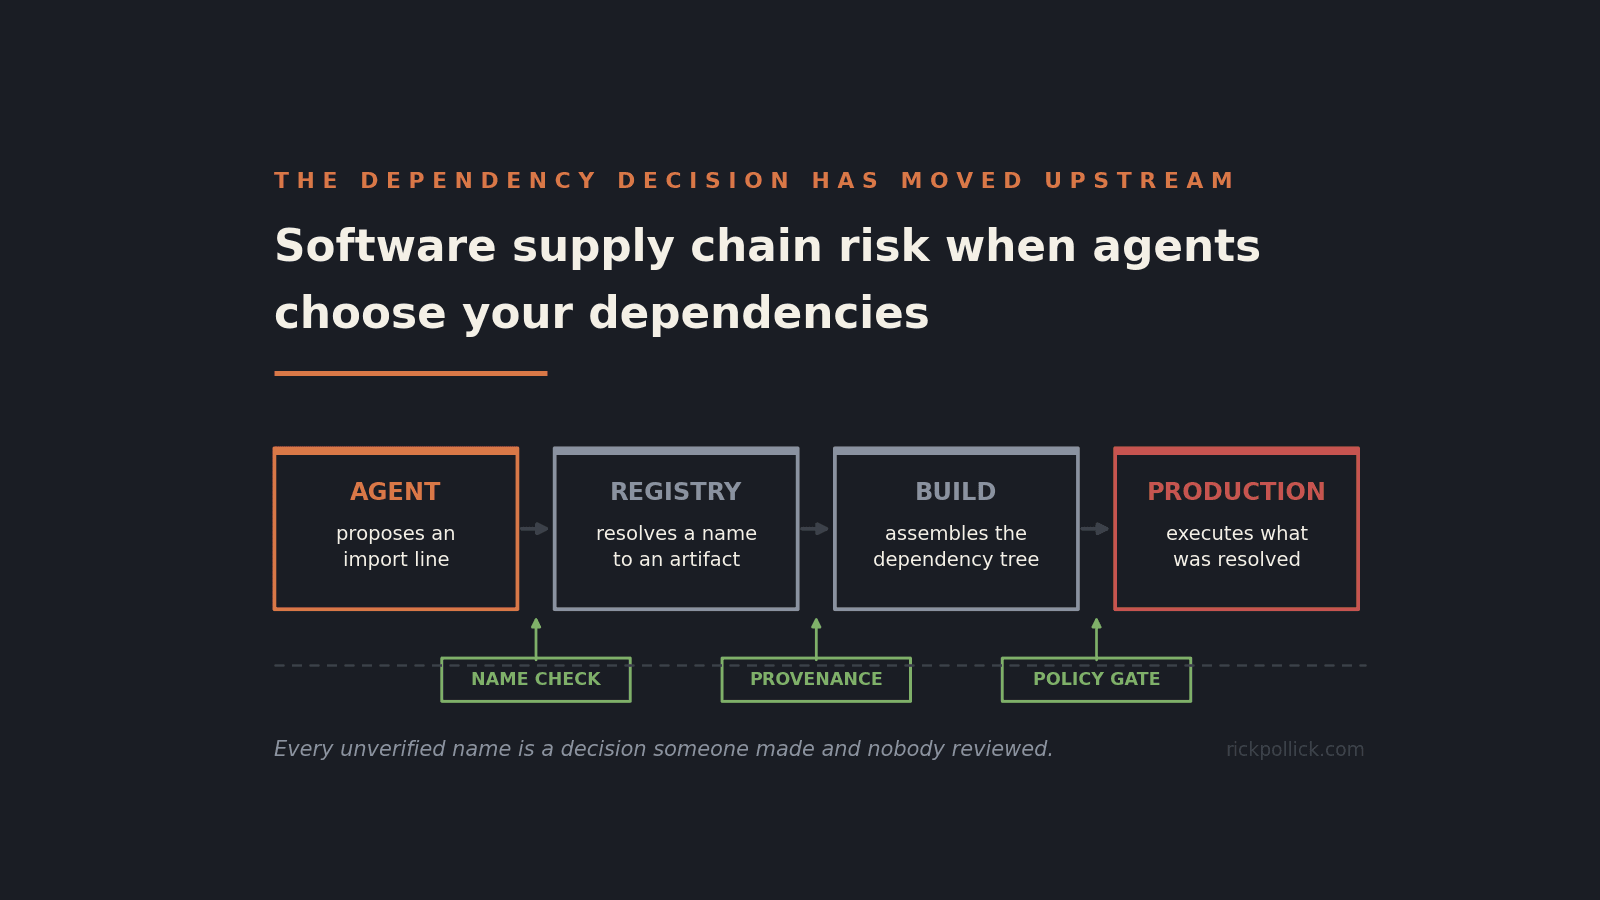
The largest security decision your organisation made last quarter was not made in a steering committee. It was an import line, written by an agent, in roughly the time it takes to blink, and it went into production because a human looked at the diff, saw code that worked, and approved it.
Members only
Keep reading for $2 / month.
The rest of this essay — along with every other members-only post, playbook, and working note — is behind a small paywall. Cancel anytime.
Payment handled by Stripe. Card details never touch this site.